Industries · Financial services
Every DDQ answer goes on the record.
Investors, consultants and bank vendor-risk teams ask for the same facts in different formats. Tribble answers DDQs, RFPs and security questionnaires from the language compliance already approved, and shows who approved each answer and when.
- 2.1Describe your valuation policy for illiquid assets. Investment opsApproved answer, reused
- 4.3Has the firm had a regulatory examination in the past five years? ComplianceApproved answer, reused
- 5.6Describe your business continuity plan and when it was last tested. OperationsApproved answer, reused
- 6.2List service providers with access to client data. SecurityApproved answer, reused
- 8.1Describe changes to the investment team since the last DDQ. Investment teamNew, sent to its owner
The documents your investors and clients send.
Grouped by who owns the answer. Every one draws on the same approved language.
| Document | What it asks for | Answer it with |
|---|---|---|
| Investment and investor relations | ||
| Investor DDQs | ILPA and AIMA questionnaires on strategy, team, valuation, operations and fees | DDQ automation → |
| Operational due diligence | Annual ODD reviews from allocators and their consultants | DDQ automation → |
| Consultant RFPs and database updates | Manager searches, often submitted through a portal | RFP automation → |
| Compliance | ||
| Regulatory and compliance sections | Examinations, disciplinary history, AML and KYC, conflicts of interest | DDQ automation → |
| Security and vendor risk | ||
| SIG and SIG Lite | The standard vendor risk assessment banks send | Security questionnaires → |
| Bank third-party risk reviews | Questionnaires built on OCC and FFIEC third-party guidance | Security questionnaires → |
| DORA questionnaires | EU operational resilience questions for ICT providers | Security questionnaires → |
Three kinds of buyer, three kinds of diligence.
Asset managers and alternatives
Allocators and consultants run operational due diligence before every mandate, then again every year.
- They send
- ILPA and AIMA DDQs, ODD questionnaires, consultant RFPs
- They check first
- Valuation, operations, team changes, regulatory history
Banks and credit unions
Vendor risk teams follow regulator guidance on third parties, so every vendor answers a long security and resilience review.
- They send
- SIG, vendor risk questionnaires, RFPs
- They check first
- Security controls, business continuity, subcontractors
Insurers
Carriers and brokers issue RFPs for services and technology, with privacy and security reviews attached.
- They send
- RFPs, security questionnaires, privacy reviews
- They check first
- Data handling, claims integration, service levels
One question, start to finish.
What happens to a single question when an investor DDQ lands.
The question
Has the firm been the subject of any regulatory examination, investigation or enforcement action in the last five years? If so, describe.
Example: investor DDQ, section 4, owned by your chief compliance officer
- 01
It comes in
The DDQ arrives as the allocator’s Word document or through a diligence portal. Tribble reads every question, including the multi-part ones.
- 02
Tribble drafts it
It finds your approved answer on regulatory history and drafts the reply in the investor’s wording.
Sourcecompliance-approved disclosure language. Approver: your chief compliance officer. - 03
Only what’s new gets reviewed
An exam closed this year, so the answer goes to your chief compliance officer with the change marked. Answers that haven’t changed go straight through.
- 04
It goes back with a record
The answers go back into the investor’s document, and you keep a record of who approved each one if an examiner asks later.
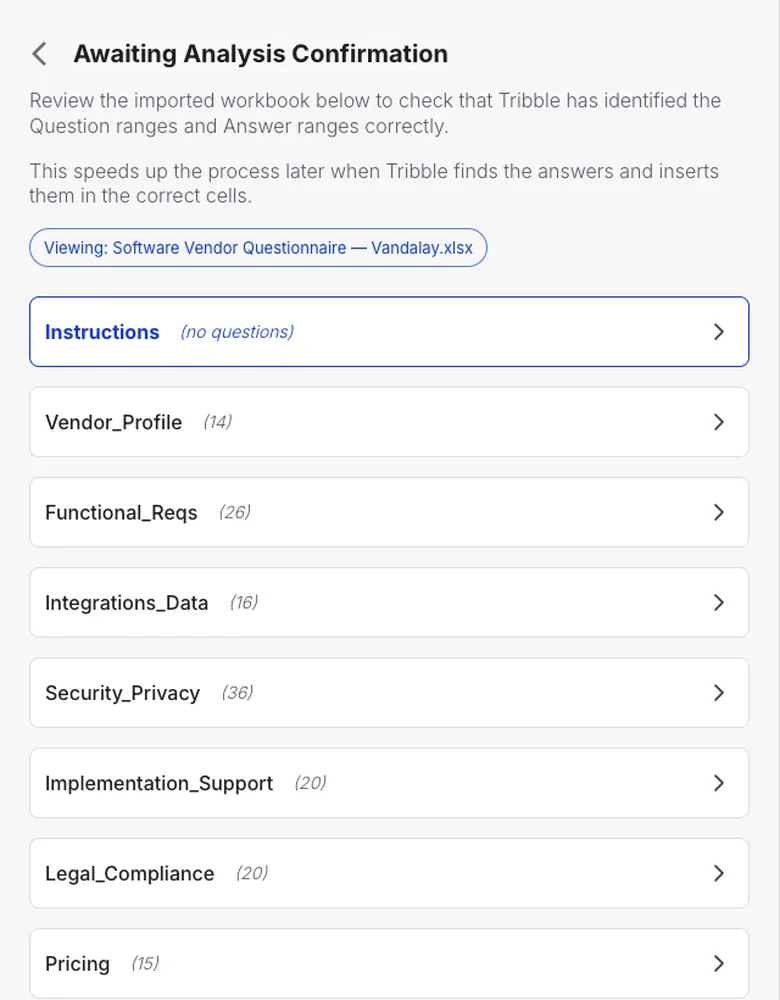
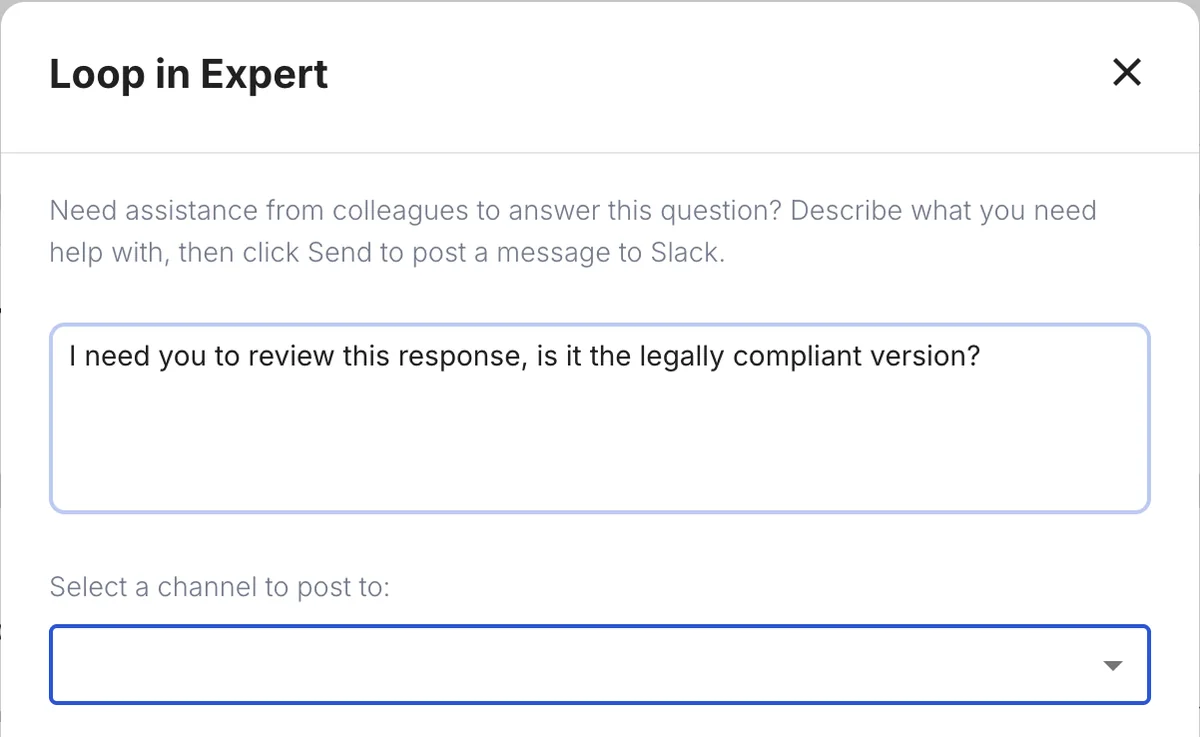
What it looks like in Tribble Respond.
The same approved language on every client call.
Relationship managers and sales teams ask Tribble Engage in Slack or Teams and get the approved answer with its source, so what a banker says on a call matches what compliance signed off.
Tribble Scribe records the call, drafts the follow-up and logs it in the CRM.
Example · Teams
@Tribble can I tell the client our fund administration is covered by a SOC 1 Type II report?
Yes. The current SOC 1 Type II report covers fund administration. Share it under NDA, and use the approved summary in writing.
Sourcecompliance-approved client statementsMapped to the frameworks your reviewers use.
- SIG and SIG LiteShared Assessments vendor risk questionnaires
- SOC 1 and SOC 2Controls reports, and what each one covers
- ILPA and AIMAStandard investor due diligence questionnaires
- DORAEU operational resilience for ICT providers
- OCC and FFIEC guidanceUS bank third-party risk management
- ISO 27001Information security management
Tribble answers from your own evidence for each framework. Tribble itself is SOC 2 Type II compliant.
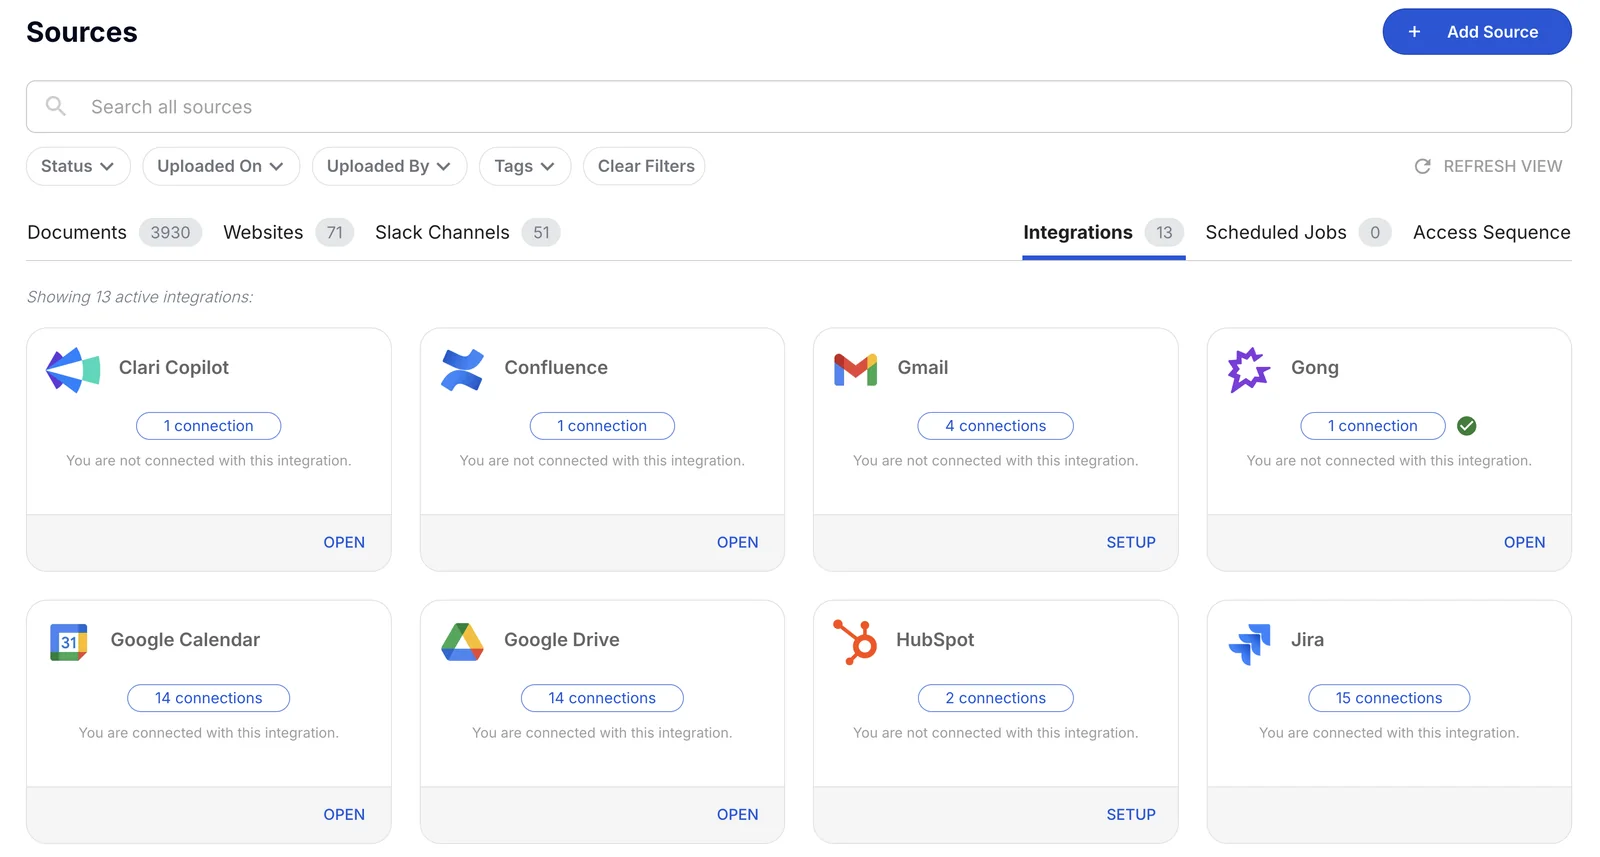
It learns from the tools your team already uses.
Policies in SharePoint, past DDQs in Google Drive, approved disclosures in Confluence, client notes in Salesforce. Tribble connects to them and keeps each one’s permissions.
Why general-purpose AI isn’t enough for regulated content.
| Compare | Generic AI | Tribble |
|---|---|---|
| Answers from | Public training data | Language compliance already approved |
| Regulatory disclosures | Guessed, or out of date | The current approved disclosure, with its approver |
| Consistency across teams | Each desk writes its own | One approved answer for every desk and region |
| When something changes | Nothing updates | Update it once and every new response uses it |
| When an examiner asks | No record | Who approved each answer, and when |
Proof from a team doing the same work.
Customer story · Revenue software
How Clari answered a 200-question RFP in under an hour
“What used to be a purely administrative process is now driving strategic insights that help us uncover product gaps and win more deals.”Brian Cody, VP, Sales Engineering, Clari Read the Clari story →
Clari isn’t a financial services firm, but its governance, risk and compliance team does the same work: long security questionnaires, specialist review and a record of every answer.
Rated by the teams that use it.
Fall 2026, across RFP, AI Sales Assistant, AI Meeting Assistants, AI Proposal Generator Tools and Sales Analytics. Read the reviews on G2 →
FAQ
Common questions.
Can Tribble keep DDQ answers consistent with our Form ADV and other filings?
Yes. Answers come from the language compliance approved, including your filed disclosures, and every answer shows its source. When a filing changes, you update the approved answer once and new responses use it.
How do we show an examiner who approved an answer?
Every answer keeps a record of its source, its approver and when it was approved. You can show exactly what was sent to an investor and who signed it off.
We run separate teams for each fund or business line. Does that work?
Yes. Answers can be approved for one fund, one region or the whole firm, and each team only sees what it’s permitted to use.
Does Tribble handle SIG and bank vendor-risk questionnaires as well as DDQs?
Yes. Security questionnaires such as SIG and SIG Lite draw on the same approved controls, so the answer in a bank’s vendor review matches the one in your DDQ.
Is Tribble secure enough for our compliance team?
Tribble is SOC 2 Type II compliant, and every source keeps its original permissions, so people only see what they’re allowed to see.
Bring your last DDQ.
Send a redacted DDQ or a recent SIG. We’ll answer it from your approved language on the call, and show you which questions would go to compliance.
Book a working session